Hollywood has no shortage of hacking scenes.
A character connects to a corporate LAN and starts typing furiously.
A terminal fills with rapidly scrolling text. Someone announces that they are "inside the network."
Seconds later, every packet, password, email, and phone call apparently becomes visible.
For network engineers, there is one obvious question: Where did the packets come from?
A packet analyzer can only analyze traffic that actually reaches it. On a switched network, opening Wireshark does not suddenly make traffic between unrelated systems visible. There first needs to be a capture point, such as a Network TAP, SPAN or mirror port, capture directly on an endpoint, or some form of inline interception.
That less glamorous part of packet capture is something movies and television often skip.
But not always. A handful of productions have actually shown, or at least described, the physical and logical mechanisms required to intercept network traffic surprisingly well.
The short answer
Literal Network TAPs are rare in movies and television. One of the clearest references appears in Alias, where an intelligence operation explicitly relies on a "network tap" physically installed at the target location. Mr. Robot goes even further in showing a believable physical interception setup, although the device involved is a rogue femtocell rather than a Network TAP. Kandahar similarly depicts operatives gaining physical access to telecommunications infrastructure before remote intelligence becomes available.
The common thread is simple: before you can analyze traffic, you need access to it. That is also how packet capture works in the real world. A Network TAP provides a dedicated copy of traffic from a network link to monitoring or capture equipment, while SPAN accomplishes traffic mirroring through the network switch.
What makes a packet capture scene realistic?
Before judging the scenes, it helps to separate two parts of packet analysis that movies frequently combine. A tool such as Wireshark is a packet analyzer. It is used to display and analyze packets captured from an interface. It does not, by itself, provide magical visibility into every conversation occurring elsewhere on a switched network.
The traffic access method determines which packets actually reach the analyzer.
That might be:
- A physical Network TAP
- A switch SPAN or mirror port
- A packet capture running directly on the target host
- An inline device
- A compromised router, proxy, gateway, or access point
- A deliberately created man-in-the-middle position
Wireshark's own documentation even describes Network TAPs as devices that can be inserted into a link to provide capture outputs without affecting the Ethernet traffic traversing that link.
For every movie scene, then, there are four useful questions: What traffic is being captured? Where is the capture point? Why would the target packets pass through it? And what receives or analyzes the resulting traffic?
With those questions in mind, Hollywood becomes considerably easier to fact-check.
1. Alias: an actual Network TAP
Alias, Season 4 Episode 17, "A Clean Conscience"
Timestamp: approximately 28:42 to 28:59
Verdict: Explicit Network TAP reference, mostly technically correct
This may be one of the most direct fictional references to a Network TAP. At approximately 28:42, Jack Bristow explains that the network tap used to intercept communications would have needed to be physically placed on the premises. The characters then discuss recovering intelligence from the installed device.
The important part is not the espionage plot. It is the recognition that interception requires access to the communications path.
That principle is correct. If you want reliable visibility into traffic traversing a particular physical network link, the monitoring infrastructure must be able to receive that traffic. A Network TAP solves that problem by creating a copy of the packets traversing the monitored connection and forwarding that copy to monitoring equipment.
There is one technical caveat in Alias. The episode treats the tap as if it stores intercepted information and can be accessed remotely later.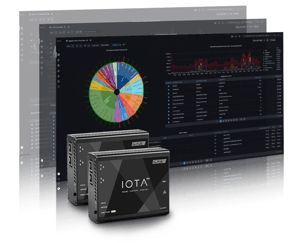
A conventional passive Network TAP does not typically store packets. Its role is traffic access. A recorder, probe, packet-capture appliance, or other monitoring system
connected to the TAP would normally perform storage and analysis.
So the fictional device is better understood as a Network TAP with capture and storage capabilities for later analysis. This is exactly what Profitap IOTA Edge models do. They allow remote access, traffic capture and storage, and even include an analysis engine built into the box.
2. Mr. Robot: building a believable interception point
Mr. Robot, Season 2 Episode 6, "eps2.4_m4ster-s1ave.aes"
Timestamp: approximately 37:45 to 38:00
Verdict: Not a Network TAP, but an excellent example of realistic traffic interception
It would be difficult to write about realistic networking on television without including Mr. Robot. In this episode, Angela is instructed to locate a workstation with a network switch underneath it. At approximately 37:45, she finds one. She installs a battery backup and a home-built femtocell, powers the device, and connects its yellow Ethernet cable to the switch. Shortly afterward, the team confirms that the femtocell is online.
Earlier in the episode, the device's purpose is explained. The femtocell behaves as a small cellular base station. The objective is to make nearby target phones connect through infrastructure controlled by the attackers, giving them an interception point for communications.
That distinction matters. This is not a Network TAP. A passive TAP observes and copies existing traffic without becoming the endpoint that attracts the communications. The femtocell attack is active. It deliberately places attacker-controlled infrastructure into the communications path.
But from a network visibility perspective, the scene gets something very important right. There is: a target traffic flow, a physical device, power, an Ethernet connection, a defined network location, and a reason why the target traffic would become observable.
The show does not simply launch a packet analyzer and assume every packet in the building becomes visible.
3. Kandahar: physical access comes before intelligence
Kandahar (2023)
Timestamp: approximately 03:35 to 03:41
Verdict: Credible physical interception, but not a conventional Network TAP
The opening minutes of Kandahar provide another unusually useful example. Tom Harris is working undercover around telecommunications infrastructure near Qom, Iran. At approximately 02:29, he asks for large cutters while working on the communications line. Around 03:35, the remote team reports that it is accessing the underground infrastructure. Seconds later, the "feeds are live," and the operation confirms that access has been established.
Later dialogue establishes that the operatives' cover involves work on telephone lines and internet connectivity.
The fictional operation appears to involve a covert telecommunications implant capable of supporting broader offensive access. That is much closer to an inline interception device or covert network implant than the passive TAPs commonly used for network monitoring.
However, the sequence captures a fundamental principle remarkably well: Remote visibility follows physical or logical access to the communications path. The intelligence team does not mysteriously acquire network traffic from a laptop hundreds of kilometers away. Someone first has to reach the infrastructure carrying that traffic.
4. The Blacklist: a packet sniffer with one missing detail
The Blacklist, Season 5 Episode 11, "Abraham Stern"
Timestamp: approximately 18:08 to 18:21
Verdict: Good definition of packet sniffing, incomplete explanation of traffic access
The Blacklist provides a useful example because it gets the terminology reasonably close while leaving out the most important networking question. At approximately 18:08, a phone is described as acting as a passive packet sniffer. The following explanation states that it can intercept and log traffic passing over a digital network.
Broadly speaking, that is what packet sniffing involves.
The missing part is: which packets can the phone actually see?
A device cannot passively observe arbitrary traffic throughout a switched Ethernet network simply because packet-sniffing software is running on it. The traffic still has to reach an interface accessible to the sniffer.
A smartphone could legitimately capture traffic available to its own interfaces, or participate in more advanced wireless or man-in-the-middle capture scenarios. But without explaining the traffic path, saying that it can simply intercept network traffic leaves out the most important part of the architecture.
Hollywood's favorite packet capture shortcut
Once you notice the capture point, many fictional hacking scenes become much less convincing. The problem is that modern Ethernet networks are switched. Traffic intended for another switch port is not normally copied to an analyst's workstation.
There are legitimate ways to obtain that visibility. A switch can mirror traffic to a SPAN port. A Network TAP can create a dedicated copy of packets traversing a link. Capture software can run on the target endpoint. Traffic can pass through a monitored gateway or proxy. An attacker might also deliberately create an interception position.
SPAN and Network TAPs solve that problem in different ways. SPAN relies on the switch to create a mirrored copy of selected traffic, while a TAP is dedicated traffic-access hardware positioned on the network link.
FAQ: Network TAPs, packet capture, and movies
What is a Network TAP?
A Network TAP, or Test Access Point, is dedicated hardware used to provide monitoring equipment with a copy of traffic traversing a network link. The copied traffic can then be sent to packet-capture, performance-monitoring, security, or analysis tools.
Is Wireshark a Network TAP?
No. Wireshark is a network protocol and packet analyzer. It analyzes packets available to its capture interface, while a Network TAP is one possible method for providing those packets to a monitoring system.
Can Wireshark see all traffic on a network automatically?
No. Wireshark can only capture traffic available on the interface it is capturing on. Monitoring traffic between other systems generally requires an appropriate traffic-access method, such as a Network TAP, SPAN or mirror port, endpoint capture, or another correctly positioned capture point.
What is the difference between a Network TAP and a SPAN port?
A Network TAP is dedicated hardware that copies traffic from a network link for monitoring. A SPAN or mirror port is configured on a network switch to send copies of selected traffic to another switch port. Both can provide monitoring visibility, but they use different traffic-access architectures.
Which TV shows portray realistic network interception?
Mr Robot: Season 2 Episode 6 contains one of the strongest examples. Angela physically installs a rogue femtocell, battery backup, and Ethernet connection near a network switch. It is not a Network TAP, but the scene realistically establishes the hardware and network position required for the interception.
Is the device in Kandahar a Network TAP?
Not in the conventional network-monitoring sense. The opening sequence is better described as covert physical interception of telecommunications or an inline network implant. It is relevant because the scene correctly shows that access to the communications infrastructure is established before remote intelligence becomes available.
Can a smartphone work as a packet sniffer?
Yes, but only for traffic accessible through its interfaces or through a network position that makes the target traffic available to it. A phone cannot automatically capture unrelated switched network traffic simply by running packet-sniffing software.
Why does the location of a packet capture point matter?
Packets must reach the capture interface before they can be recorded or analyzed. Placing traffic-access infrastructure at the correct point in the network determines which conversations are visible to the monitoring system.
Do Network TAPs store captured packets?
A conventional passive Network TAP primarily provides access to network traffic by copying packets toward monitoring equipment. Packet storage is typically handled by the connected capture, recording, probing, or analysis system rather than by the passive TAP itself.